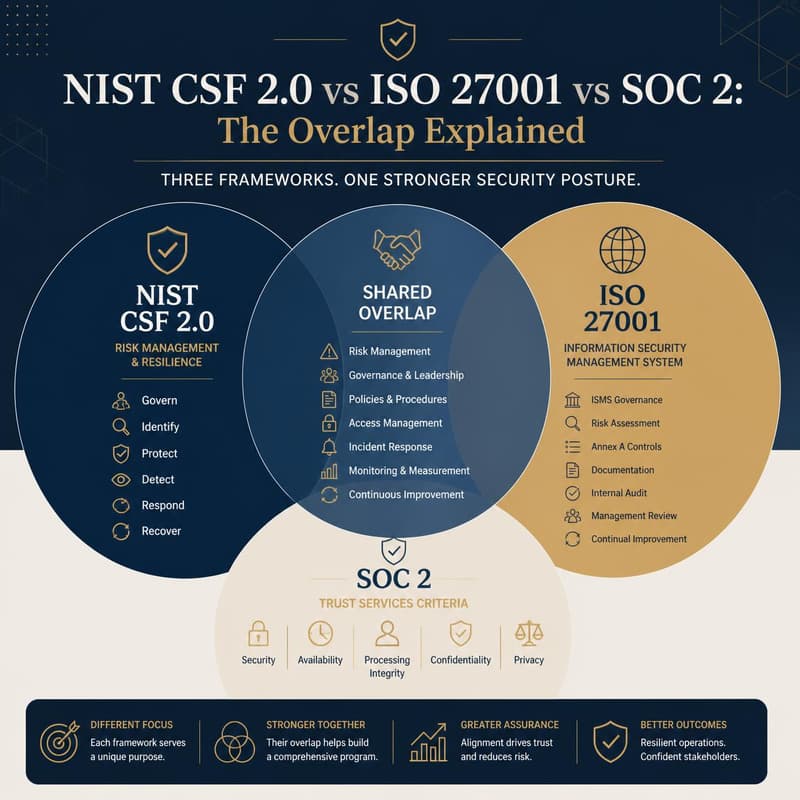

NIST CSF 2.0, NIST AI RMF, ISO 27001, SOC2: The Overlap Explained
Most companies build their compliance program three times.
Once for NIST CSF 2.0. Then they re-map for ISO 27001. Then they re-map again for SOC 2 Type II. Three control libraries. Three evidence inventories. Three owners.
It is the most expensive mistake in mid-market GRC, and the data backs it up. AICPA mapping shows roughly 80% of SOC 2 controls overlap with ISO 27001. NIST published crosswalks show 83% of NIST CSF 2.0 requirements are satisfied by ISO 27001 alone.
If 80% of the work is the same, why build three programs?
In this one-hour live advisory, I walk through the Build Once, Map to All methodology I use with clients to design unified GRC programs that satisfy NIST CSF 2.0, ISO 27001, and SOC 2 Type II simultaneously, with shared evidence and a single source of truth.
What we cover:
- The control overlap between the regulatory framework
- The Build Once, Map to All control library approach
- Audit and Regulatory requirements you need to prep and evidence for
- Additionally topic: The EU AI Act coverage and documentation
- Live Q&A on your specific framework stack
Who it is for: CISOs, GRC managers, fractional security leaders, founders mid-build on any compliance program.
You will leave with a downloadable NIST CSF ISO 27001 SOC 2 Crosswalk Quick Reference, plus the option to book a 30-minute follow-up.
Hosted by Meenu Chadha, founder of Cyber Advisory and fractional vCISO.