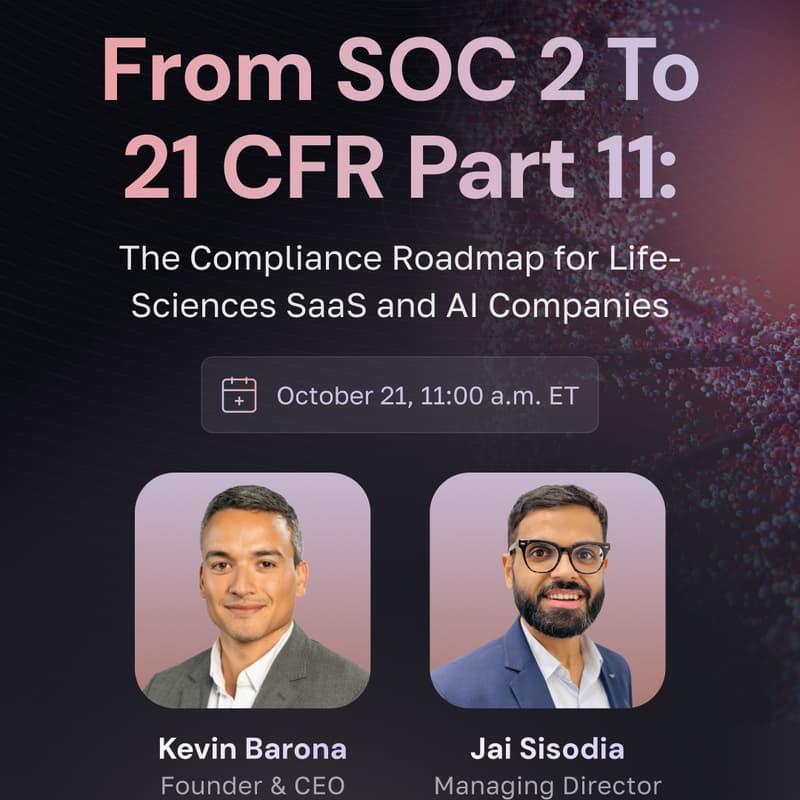

From SOC 2 to 21 CFR Part 11: The Compliance Roadmap for Life-Sciences SaaS and AI Companies
Free live webinar · Wednesday, October 21, 2026 · 11:00 a.m. ET
45-minute session + 10–15 minutes of live Q&A
Registration is on the Cycore site: https://www.cycoresecure.com/webinars/the-compliance-roadmap-for-life-sciences-software-companies
Register there to receive joining instructions, reminders, the replay, and the resource pack.
Your next pharma or biotech customer may ask for more than SOC 2: validation documentation, audit trails, quality procedures, or evidence supporting electronic-record requirements. What can you reuse from your existing security program, what additional work is needed, and what should you prioritize before the customer review?
Join Cycore for a practical walkthrough of the security, quality, and validation requirements SaaS and AI companies encounter when selling into life sciences, and leave with a clearer path from customer questions to an actionable compliance plan.
What you'll learn
Understand the requirements. How SOC 2, ISO 27001, and 21 CFR Part 11 fit into the customer-review process, and where ISO 9001, EU Annex 11, GAMP 5, and ISO 42001 enter the conversation.
Reuse the work you've already done. Which controls and evidence may support additional customer requirements, which need strengthening, and where you may need new processes or product capabilities.
Understand what regulated use adds. Intended use, validation support, audit trails, electronic signatures, and record retention, including how vendor and customer responsibilities differ.
Prioritize your next 90 days. Identify a starting point based on your current program, product, and customer requirements, illustrated through an anonymized AI software vendor's experience with a pharmaceutical customer's supplier audit.
Who should attend
Founders, CTOs, COOs, product and engineering leaders, and security, quality, or compliance teams serving pharmaceutical, biotechnology, clinical research, and laboratory organizations. Especially relevant if you are:
Entering the life-sciences market and deciding where to start
Pursuing SOC 2 or ISO 27001 and planning your next steps
Already operating a security program and receiving quality or validation requests
Preparing for a customer's supplier review or audit
Speakers
Kevin Barona, Founder & CEO, Cycore
Jai Sisodia, Principal Advisor, Cycore
Every registrant receives
The webinar replay plus a resource pack: compliance roadmap, applicability planning checklist, control crosswalk, representative customer request list, and 90-day planning worksheet, whether or not you attend live.
Save your seat: https://www.cycoresecure.com/webinars/the-compliance-roadmap-for-life-sciences-software-companies