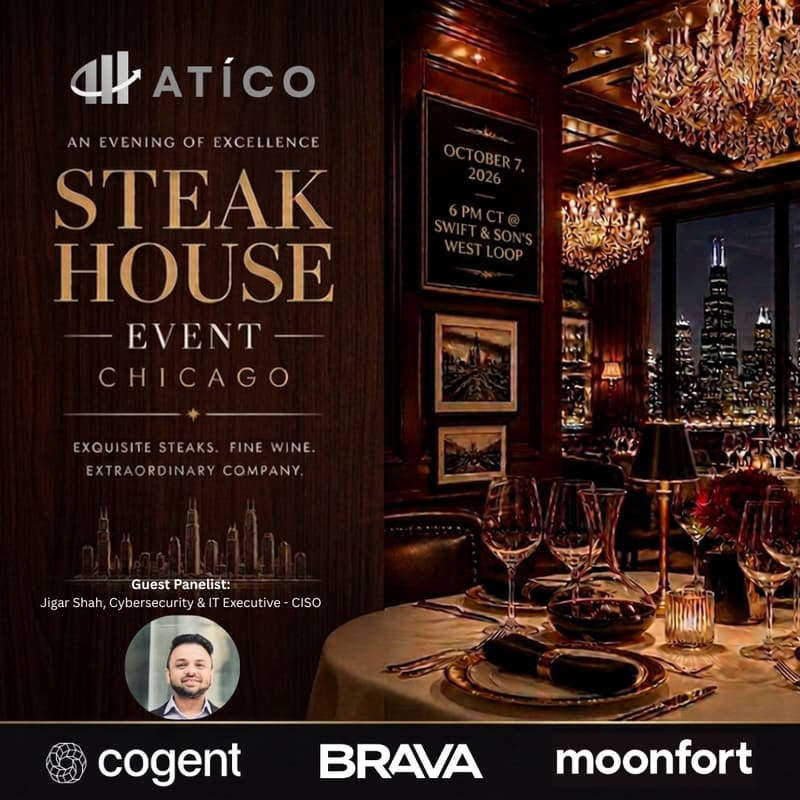
The steak is the setting. The conversation is the reason.
The steak is the setting. The conversation is the reason.
A small, off-the-record table of Chicagoland CIOs and CISOs, built around two questions most teams are quietly sitting with: how much of your SIEM spend you never actually use, and where you can trust AI agents to run on their own.
More money in. Less signal out.
Security spend keeps climbing while visibility drops. Telemetry grows faster than the budget to act on it, and the tools meant to store and watch it are the most expensive, and the hardest to leave, in the stack. Every new tool is one more contract, one more integration, one more renewal to defend. At the same time, agentic tooling is moving into security operations faster than most teams have defined where to trust it.
For CIOs, that's unbudgeted infrastructure risk and a harder story for the board. For CISOs, it's blind spots that only surface at an audit or an incident.
The question on the table: Can you take the cost out of your security data and tooling, consolidate vendors, and modernize the stack, without a migration project and without opening new blind spots?
Your host for the evening
Jigar Shah, CISO at Medusind, two decades leading IT, data, and cybersecurity.
Not a vendor host. A peer who has run the programs you're running. Jigar has spent twenty years leading security, data, and technology for large, heavily regulated organizations across healthcare, financial services, banking, and retail. He's stood up cybersecurity departments from scratch, led enterprise cloud migrations and M&A integrations worth $15M+ in synergies, and cut service-delivery costs 70% through automation. A law grad and MBA, he brings a rare blend of tech, business, and legal fluency, and he's the kind of CISO who can take any of it to a board without hiding behind a slide.
Two questions we'll actually work through
Paying to store what never fires. You're paying premium rates to store telemetry. How much of it has ever produced a detection, and could you actually walk away from the platform holding it? Cutting log sources to control SIEM spend just trades cost for blind spots. Getting both means modernizing, ideally without a migration. Brava joins us on this one: they cut SIEM ingestion cost by offloading telemetry to low-cost, searchable storage and applying intelligence in the pipeline before it reaches the SIEM.
Where you let agents run alone. Most teams are piloting agentic security operations. Fewer can say where they actually trust an agent to run without a human in the loop, where they pulled it back, and who owns the outcome when it's wrong. Moonfort joins us here: they're building cloud-native detection that runs autonomously where it's safe, with the human-in-the-loop boundary as a first-class control.
What the evening is (and isn't)
No slides. No demos. Off the record. One table of peers who own both the risk and the budget.
You should leave with at least one specific thing you can act on Monday, and a few people worth calling later.
Seats are limited and requests are reviewed so the table stays balanced. If you'd like one, request to join and we'll be in touch.