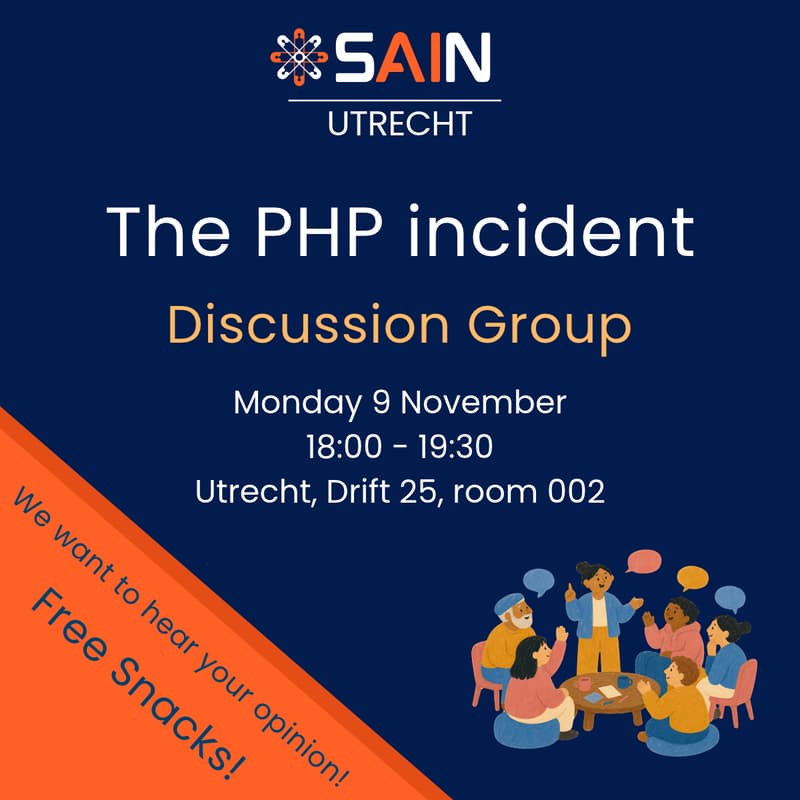

Discussion group - The PHP incident
When AI finds the bug first: who governs the window?
On 21 October 2026, PHP, the programming language behind roughly 70% of websites, released emergency fixes for two critical flaws, together called PHP2Shell. Researchers found them with frontier AI models, including OpenAI's GPT-5.6 Sol and Google's Gemini 4 Argon. In the Netherlands, the NCSC, DigiD, MijnOverheid, the Tweede Kamer and parts of the higher-education network went offline as a precaution. OpenAI presents the case as AI finding the flaws before attackers did, and has proposed a five-stage process for coordinating such disclosures, with governments brought in along the way. Yet the embargo broke early, exploit attempts appeared days before disclosure, and the researcher who found the first flaw says he used publicly available models. This week we ask who should govern the window between an AI finding a flaw and the world patching it. We pair the news with a June 2026 expert consultation by the US National Academies, which expects AI to favour attackers in the near term and finds that defensive work such as patch deployment is the hardest part to speed up.
Questions we'll explore
Did AI help defenders or attackers more in the PHP incident? How would we know?
Should a private AI lab coordinate a global security response and decide who hears first? If not, who should?
Were the Dutch precautionary shutdowns, from DigiD to the Tweede Kamer website, proportionate?
Should access to the most capable cyber models be restricted, and who should decide who gets it?
The National Academies find that patch deployment is the hardest part of defence to speed up. What would help the Netherlands patch faster?
Format (90 min): Discussion in small groups and plenary. No presentations, no wrong questions.
Readings:
How to prepare: This is a standalone session; no lecture needed. Please reserve about 1.5 hours, ideally over a few evenings. Short on time? The ★ items (about 1 hour) are the essentials.
Part 1 (~35 min): what happened
★ ~10 min: AP, Websites scramble to fix software flaw that could put much of internet at risk
★ ~5 min: NL Times, Some important Dutch websites still offline after PHP issues
~10 min: BCS, Analysis: the global PHP incident, the view of the UK professional body for IT
~10 min: AI Weekly, PHP2Shell roundup, on the credit dispute, the broken embargo and early exploitation
Part 2 (~35 min): the academic lens
★ ~15 min: OpenAI, Coordinated disclosure of critical vulnerabilities, the five-stage process. No time? Read the PPC Land summary instead.
★ ~20 min: National Academies of Sciences, Engineering, and Medicine (2026), Implications of AI for Cybersecurity: A Rapid Expert Consultation. Read the chapter Artificial Intelligence and the Changing Cybersecurity Landscape (pp. 4–7).
Optional: Shevlane & Dafoe (2020), The Offense-Defense Balance of Scientific Knowledge: Does Publishing AI Research Reduce Misuse?, AAAI/ACM Conference on AI, Ethics, and Society (~30 min). On when disclosure helps defenders more than attackers.
Part 3 (~15 min): reflection
★ ~15 min: note whether you think AI helped defenders or attackers more in this case, one stage of OpenAI's five-stage process you would rather give to a public body than a company, and one finding from the National Academies that the PHP incident confirms or contradicts
Attendees consent to filming and photography as participants in this event. By attending, you agree to being filmed or photographed, which may be used for social media, website, and newsletter content. If you wish to attend but do not want to be photographed, please during the event let a member of our staff know so we can accommodate this.