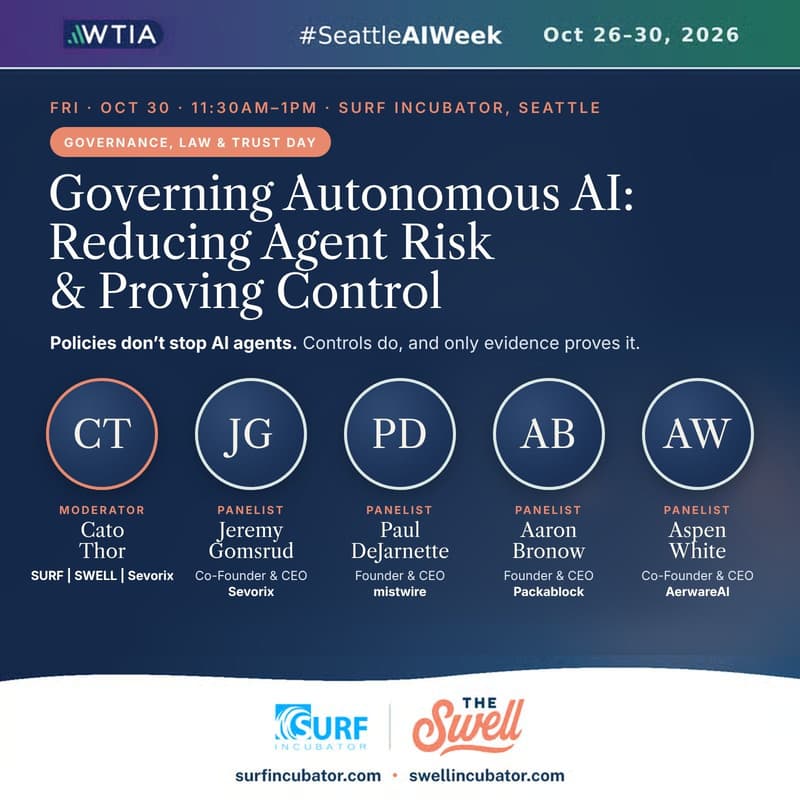
Governing Autonomous AI: Reducing Agent Risk & Proving Control
Your registration answers (optional) shape the discussion.
An AI agent doesn't need a hacker or a stolen password to cause damage. It only needs the access it was given, and a task that takes it further than anyone expected.
That's why AI governance is shifting from principles to proof. Cyber insurers now ask about AI controls at renewal, and regulators increasingly want evidence, not intentions. The question is no longer "do you have an AI policy?" It's "can you show what your agents actually did, and what stopped them?"
Five founders building AI security and governance tools break down where agent risk really comes from, which controls reduce it, and how to produce evidence that holds up with auditors, insurers, and regulators. We'll also be candid about what nobody can prove yet.
You'll leave with:
What does governance, risk, & control really mean?
Case studies where it mattered
How does AI risk impact you?
Audience answers drive the convo
Stories from experts on 4 layers of AI risk
Multiple approaches: same goal
Your role in preventing AI risk in your work/business
Resources to identify & control AI agent risk
Who it's for: founders and engineering leaders deploying AI agents, in-house counsel, GRC and compliance leads, CISOs and security teams, cyber insurance brokers and underwriters.
Main stage, 70-minute panel + 20-minute open Q&A.
Beverages, cheese, crackers, and other light snacks provided.