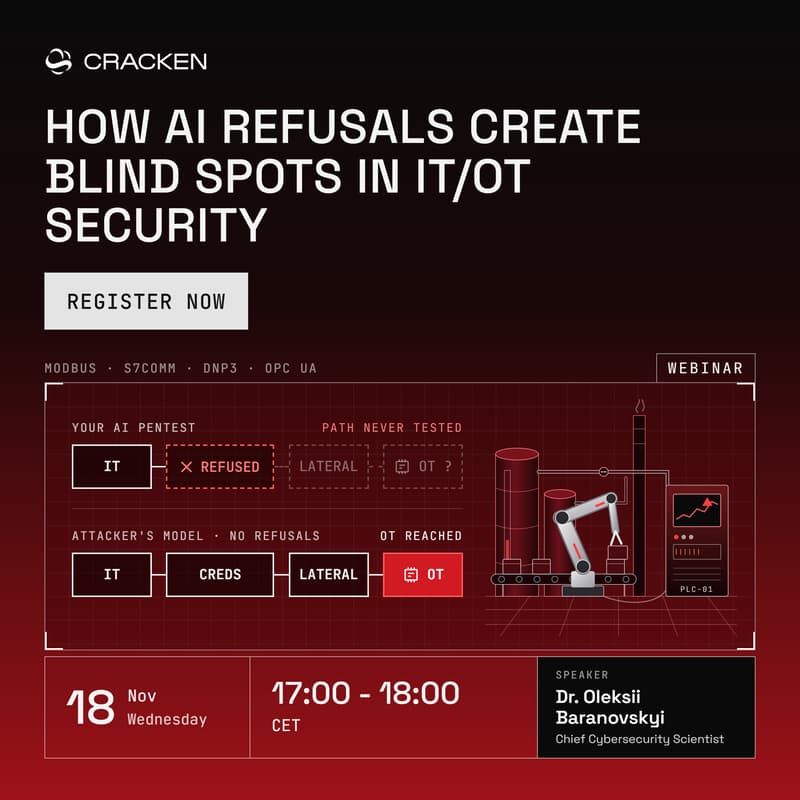

How AI Refusals Create Blind Spots in IT/OT Security
In offensive security, an AI refusal isn’t a safety feature. It’s a path that never got tested. In IT/OT environments, untested paths are exactly where the most damaging intrusions happen, and the models attackers use don’t refuse.
In this live session, Dr. Oleksii Baranovskyi, Chief Cybersecurity Scientist at Cracken, explains how refusals in AI-assisted testing quietly weaken security programs, and what that means for teams protecting critical infrastructure.
What he’ll cover:
1. False assurance
When an AI model refuses or silently skips a step, the report shows “no finding.” Leadership reads that as “secure,” and the path to OT stays open.
2. Coverage gaps where it matters most.
Refusals cluster around the highest-impact steps: credential abuse, lateral movement, and ICS protocol interaction. Those are the exact points where an attacker crosses from IT into OT.
3. Wasted operator time and inconsistent results.
Teams burn hours re-prompting, and two runs of the same test produce different coverage. That undermines the repeatability that audits and frameworks such as NIS2, DORA/TLPT and IEC 62443 depend on.
4. Attacker asymmetry.
Adversaries run unrestricted or fine-tuned models. A defender held back by refusals is testing against a weaker threat than the real one.
Who should attend.
Red team leads, offensive security practitioners, OT/ICS security owners, and CISOs who rely on AI-assisted testing to make risk decisions.