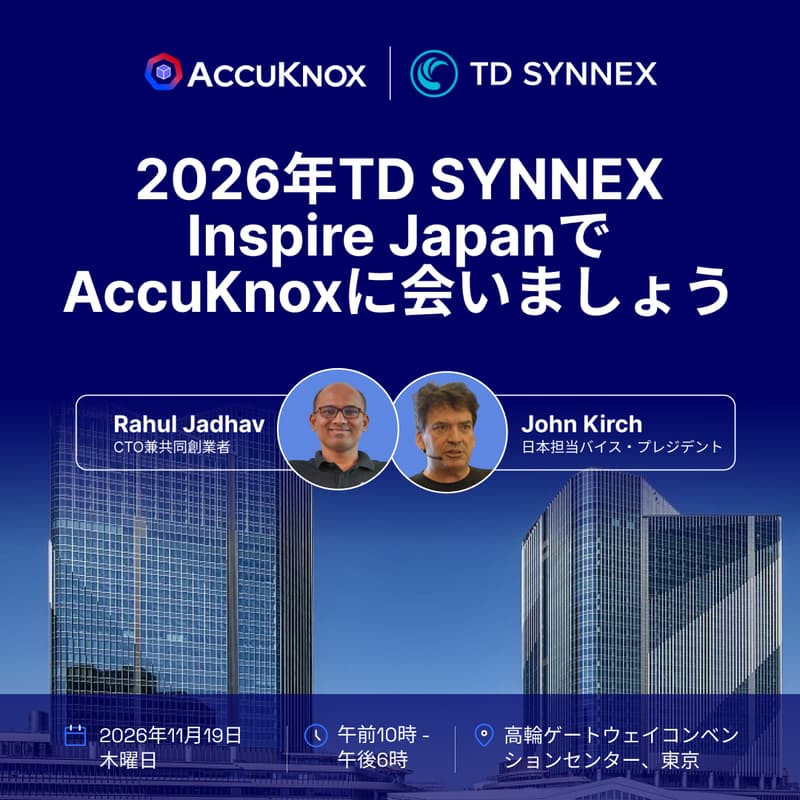

TD SYNNEX Inspire Japan 2026:マルチクラウド環境におけるAIセキュリティ
ハイブリッドAI環境における可視性の盲点
オンプレミス、プライベートクラウド、マルチクラウド環境にまたがってAIを運用する日本企業が、「何がどこで稼働しているのか」「誰がアクセスできるのか」「データやモデルが環境間をどのように移動しているのか」を統合的に把握できていない現状について解説します。AIワークロードにおいて境界型セキュリティが機能しない理由
AIシステムが複数のインフラ環境にまたがることで、従来のネットワーク境界によるセキュリティが機能しにくくなる理由と、それがリスクの拡大にどうつながるのかを解説します。実践的なセキュリティ基盤としてのゼロトラスト
AIがどこで稼働しているかにかかわらず、すべてのワークロード、アイデンティティ、AIとツール間のインタラクションを検証するゼロトラストの考え方を紹介します。LSS、eBPF、KubeArmorを活用したランタイム保護についても取り上げます。AIシステムのサプライチェーン可視化
SBOMおよびxBOMのプラクティスをAI領域へ拡張し、AIスタック全体におけるコンポーネントと依存関係を追跡する方法を解説します。AI固有のリスク領域を保護する
モデルへのアクセス制御、プロンプトとデータフローの監視、AIエージェントとシステム間の通信セキュリティなど、AI特有のリスク領域への対策を紹介します。最後に、参加者が自社のAI環境に適用できるリファレンスモデルを提示します。
登壇者:
Rahul Jadhav — CTO & Co-founder, AccuKnox
John Kirch — Vice president,Japan,AccuKnox
The hybrid AI blind spot. Why Japanese enterprises running AI across on premise, private cloud, and multi cloud environments often lack unified visibility into what's running where, who has access, and how data and models move between environments.
Why perimeter security fails for AI workloads. A look at why traditional network boundaries break down when AI systems span infrastructure types, and what that means for risk exposure.
Zero Trust as the practical baseline. Verifying every workload, identity, and AI to tool interaction regardless of location, covering runtime protection through LSS, eBPF, and KubeArmor.
Supply chain visibility for AI systems. Extending SBOM and xBOM practices to track components and dependencies across the AI stack.
Securing AI specific risk surfaces. Model access controls, prompt and data flow monitoring, and agent to system communication security, closing with a reference model attendees can apply to their own environments.
Speakers :
Rahul Jadhav - CTO & Cofounder, Accuknox
John Kirch - Vice president,Japan, Accuknox