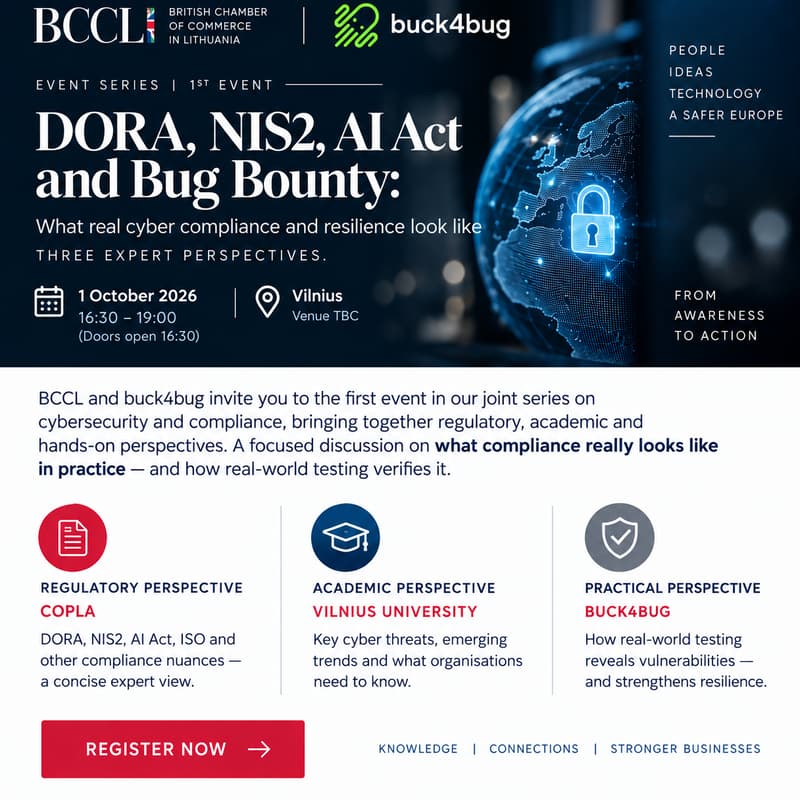
DORA, NIS2, AI Act & Bug Bounty: What Real Cyber Compliance & Resilience Look Like
Cybersecurity is no longer simply an IT issue — it is a business, regulatory and resilience priority.
BCCL and Buck4Bug are launching a joint event series for the Lithuanian business community, bringing together three expert perspectives to explore what cyber compliance and resilience actually look like in practice.
In one focused session, we will connect the regulatory, academic and hands-on cybersecurity perspectives, looking beyond compliance checklists to understand where organisations are genuinely exposed — and how real-world testing can reveal the gaps.
THREE EXPERT PERSPECTIVES
REGULATORY | COPLA
An expert perspective on DORA, NIS2, the AI Act, ISO and other compliance requirements, focusing on the practical nuances regulated organisations need to understand.
The proposed Copla speaker is Nojus Antanas Bendoraitis, Chief Legal Officer & Director of Regulatory Compliance Solutions and co-founder, who is directly responsible for compliance expertise. The final speaker confirmation is pending.
ACADEMIC & RESEARCH | VILNIUS UNIVERSITY
Prof. Dr. Linas Bukauskas, Professor and Head of the Cyber Security Laboratory at Vilnius University, will bring an academic and research perspective to the discussion.
His work focuses on cyber threats and vulnerabilities, security-system implementation and the analysis of real-world intrusion data. He also develops educational platforms for security risk assessment and training and has contributed expert commentary on cybersecurity threats facing Lithuania.
PRACTICAL TESTING | BUCK4BUG
Paulius Šliavas, Founder & CEO of Buck4Bug, will bring the perspective of hands-on cybersecurity testing.
Paulius founded Buck4Bug, the first bug bounty platform in the Baltics, focusing on penetration testing and bug bounty programmes delivered through a vetted community of ethical hackers. In 2026, Buck4Bug also launched a partnership with Copla, connecting real-world security testing with automated compliance evidence.
FROM COMPLIANCE TO REAL RESILIENCE
The discussion will explore:
What DORA, NIS2, AI Act and ISO requirements really mean for businesses
What auditors and security testers actually look for
Where organisations most commonly have security gaps
How penetration testing and bug bounty programmes can expose vulnerabilities
How businesses can move from compliance on paper to genuine cyber resilience
What C-level leaders, security, compliance and risk professionals should be paying attention to now
The event will conclude with a panel discussion and audience Q&A, followed by networking.
WHO SHOULD ATTEND?
The event is particularly relevant for BCCL members, C-level executives and professionals working in IT, cybersecurity, compliance and risk management, especially those representing financial services, technology and other regulated sectors.
WHY ATTEND?
Three perspectives. One conversation. Practical takeaways.
Gain a concise view of the regulatory landscape, hear from one of Lithuania's leading academic cybersecurity experts and understand how real-world testing reveals vulnerabilities that compliance frameworks alone may not uncover.
Most importantly, connect directly with Lithuania's cybersecurity ecosystem and the wider UK–Lithuania business community.
From awareness to action. From compliance to resilience.
BCCL × Buck4Bug
Knowledge. Connections. Stronger businesses.