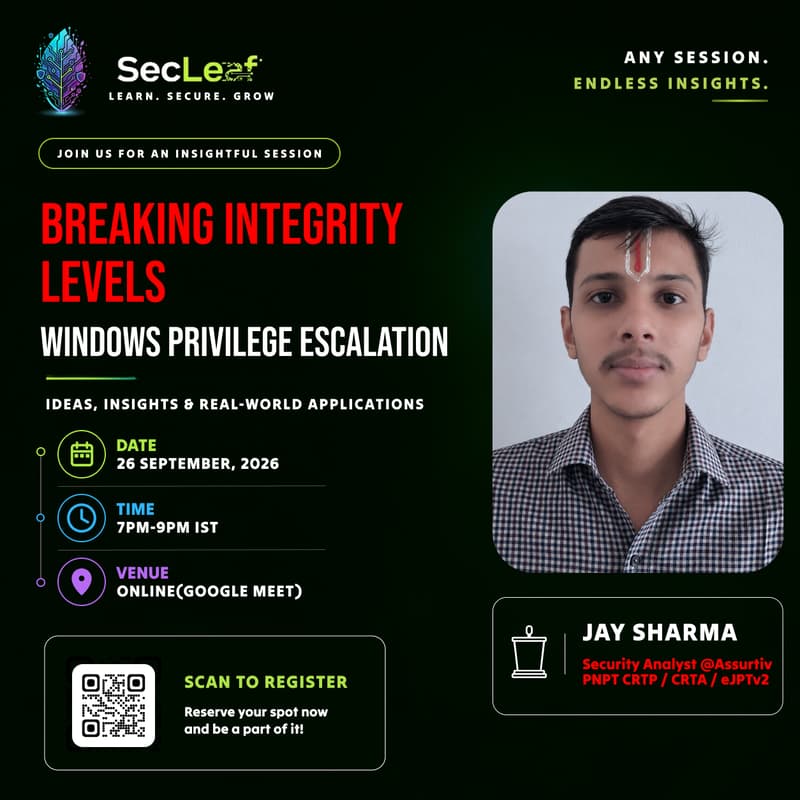
Windows UAC Security & UAC Bypass: A Technical Deep Dive into Integrity Levels and Access Tokens
Join SecLeaf for an interactive Windows UAC Security and UAC Bypass session designed to provide a technical understanding of User Account Control (UAC), Windows Integrity Levels, Access Tokens, Mandatory Integrity Control (MIC), and privilege escalation.
This technical deep dive takes you from the fundamentals of Windows security architecture to the practical concepts behind UAC bypass techniques and privilege boundaries. You'll learn how Windows manages administrator privileges, how access tokens and integrity levels control security decisions, how UAC elevation works, and how security professionals can detect and mitigate UAC bypass and privilege escalation attempts.
What You'll Learn
Introduction to Windows User Account Control (UAC)
Purpose of UAC in Windows Security
Understanding Windows Integrity Levels
Access Tokens and Windows Security Contexts
Mandatory Integrity Control (MIC)
Privilege Separation in Windows
UAC Architecture and Admin Approval Mode
Split Tokens and Administrator Accounts
Understanding the Windows UAC Elevation Process
How UAC Bypass Techniques Work
Common UAC Bypass Mechanisms and Their Underlying Concepts
UAC Bypass from an Attacker and Red Team Perspective
Detecting UAC Bypass and Privilege Escalation Attempts
Security Indicators Associated with UAC Bypass
UAC Security Controls, Detection and Mitigation
Practical Demonstration of a Controlled UAC Bypass
Analyzing Windows Integrity-Level Transitions
Q&A and Technical Discussion
Who Should Attend
Cybersecurity Students
Beginners interested in Windows Security
Aspiring SOC Analysts
Penetration Testing and Red Teaming Enthusiasts
Cybersecurity Researchers
Security Professionals interested in Privilege Escalation
Anyone interested in understanding Windows UAC and security architecture
What You'll Gain
By the end of the session, you'll have a practical understanding of how Windows UAC works, how Access Tokens and Integrity Levels enforce privilege boundaries, how UAC Bypass techniques attempt to circumvent these security controls, and how security teams can detect and mitigate suspicious privilege escalation activity.
The practical demonstration will connect Windows security concepts, UAC architecture, privilege escalation, and UAC bypass detection with a controlled security scenario, helping you understand how these techniques are analyzed from both offensive and defensive perspectives.