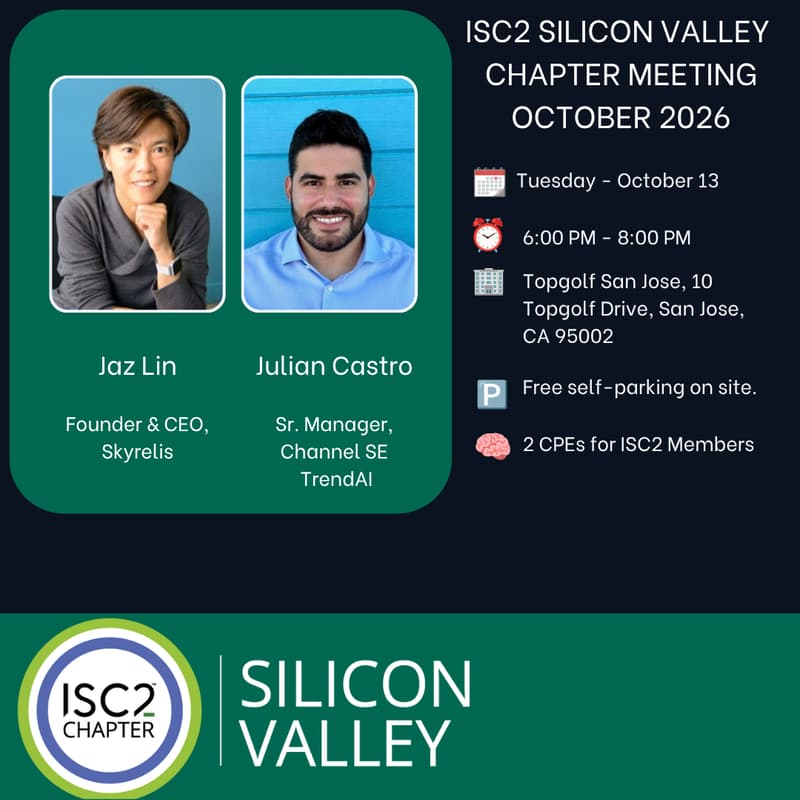

ISC2 Silicon Valley - October 2026 Chapter Meeting
🙏 Thank you to TrendAI for making this month's meeting possible.
Join the ISC2 Silicon Valley Chapter for our October 2026 meeting — and this month we're doing it at Topgolf. Last month we looked at what agentic access does to identity. This month picks up where that left off. The agent isn't just reading anymore; it's calling tools, updating records, and triggering workflows. Two sessions on what that means for control: how you govern and prove what an agent is permitted to do, and how you find and prioritize the exposure underneath it all while attackers move faster than your remediation capacity.
🎤 Session 1 | When AI Agents Can Act: Can You Actually Control What They Do?
Jaz Lin, Founder and CEO, Skyrelis
Red teams are showing that AI agents can be hijacked, misdirected, and pushed into taking actions nobody intended. As agents gain the ability to access enterprise data, call tools and APIs, update records, trigger workflows, and operate across internal systems, SaaS platforms, and browser environments, security teams face a different control problem.
The old question — can this identity access this data? — is no longer enough. The new question is: what is the agent allowed to do with that data, under whose policy, and can the organization prove it?
Rather than treat the problem as an abstract AI policy discussion, Jaz introduces a six-area Agentic Security Readiness Scorecard: agent inventory and control boundary, tool and action visibility, autonomy and approval, sensitive-data exposure, runtime policy enforcement, and audit-ready evidence. Using a realistic enterprise workflow, the session shows how teams can move from broad policy statements to concrete runtime decisions.
Attendees will be able to apply the six-area Agentic Security Readiness Scorecard to assess their own environment across inventory, action visibility, autonomy, data exposure, runtime enforcement, and evidence; determine for a given agent action whether it should be allowed, blocked, masked, escalated for approval, or required to produce vendor evidence; and work a single high-risk workflow through an Inventory → Prioritize → Govern → Prove path to identify the first control gap that matters and decide what needs direct runtime control versus vendor-enforced proof.
Bring one high-risk agent workflow in mind, and bring your hard cases.
About the Speaker
Jaz Lin is the Founder and CEO of Skyrelis. A CCIE and cybersecurity product leader, she brings more than two decades of experience across network security, cloud security, endpoint security, and SASE, with leadership experience at Cisco, VMware, Rubrik, and Intrado. In her previous role, Jaz experienced firsthand the operational, control, and ownership challenges that emerge when AI agents move into real business workflows. She founded Skyrelis to solve the problem she had lived: how to maintain visibility, control, and accountability as AI agents become more autonomous.
🎤 Session 2 | Session details to follow
Julian Castro, Sr. Manager, Channel Systems Engineering, TrendAI
About the Speaker
Julian Castro is Senior Manager, Channel Systems Engineering at TrendAI. He works alongside channel partners to help joint customers operationalize risk management — not just buy tools, but measurably reduce cyber risk. His focus is on helping organizations identify exposure, understand business impact, and prioritize what to fix first.
📅 Tuesday, October 13, 2026
🕕 6:00 PM – 8:00 PM PT
📍 Topgolf San Jose, 10 Topgolf Drive, San Jose, CA 95002
Level 3, Chairman's Suite
🎓 CPE-eligible
Dinner
Provided — boneless wings, cheese and charcuterie, BBQ meatballs, queso blanco with chips, spinach artichoke dip, and donut holes, with fountain soda, iced tea, coffee, and water. Vegetarian options available. Topgolf cannot guarantee allergen-free preparation.
Bay Time
⛳ Free bay time after the sessions, 8:00 PM to 10:00 PM. Spots are limited, so grab one early. Everyone is welcome for the sessions and dinner regardless.
🙏 Help spread the word — repost and invite your network across the cyber community
🤝 Join the Community: Open Google Form
🎙️ Speaker Opportunities — Open Call
ISC2 Silicon Valley is booking sessions through Q4 2026, and we're opening the mic to the wider cybersecurity community. Not an ISC2 member? Doesn't matter. If you've got something worth sharing, we want you on our stage.
Hard-won lessons. Fresh research. War stories you can finally talk about. First-time speakers and seasoned presenters all welcome.
⏱️ Up to 40 minutes + Q&A
📍 In-person at our monthly meeting
🎓 CPE-eligible for attendees