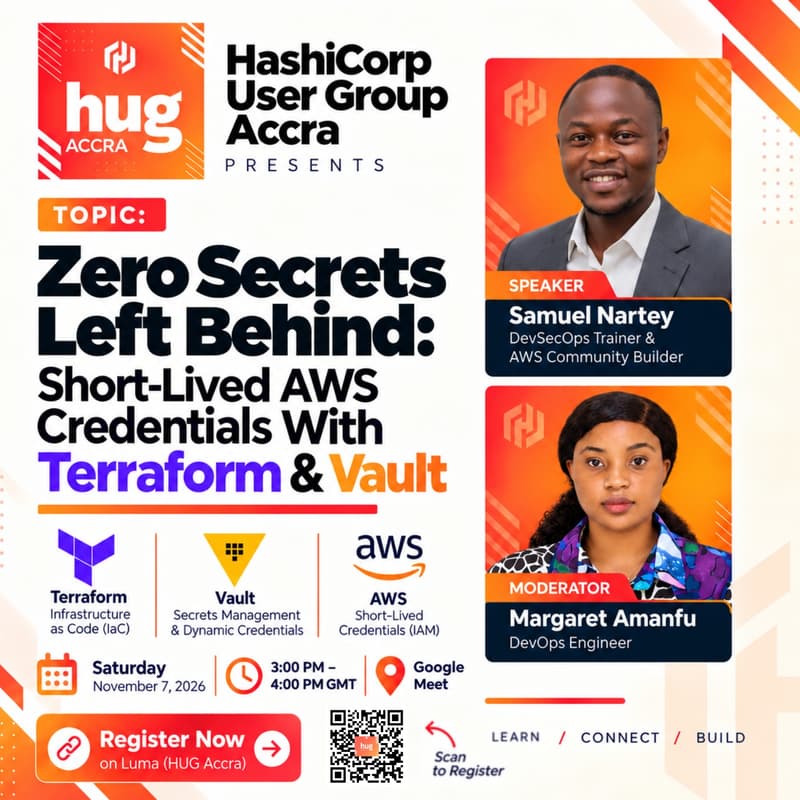

Zero Secrets Left Behind: Short-Lived AWS Credentials with Terraform & Vault
A leaked credential can put your entire cloud environment at risk. Even when secrets are stored carefully, long-lived credentials can introduce unnecessary security risks.
Join HashiCorp User Group Accra (HUG Accra) for a practical session exploring how Terraform, HashiCorp Vault, and AWS IAM work together to improve secrets management and enable the use of short-lived credentials.
What we'll explore
The risks of long-lived AWS credentials
How HashiCorp Vault supports secrets management
How Terraform and AWS IAM fit into a more secure credential workflow
Practical approaches to reducing credential exposure
Who should attend?
AWS users, Terraform practitioners, DevOps engineers, cloud engineers, security professionals, and anyone looking to strengthen their cloud security practices.
Whether you're just starting with Terraform or already managing AWS infrastructure, come ready to learn, ask questions, and connect with the community.
Event details
📅 Date: Saturday, November 7, 2026
⏰ Time: 3:00 PM – 4:00 PM GMT
📍 Location: Online via Google Meet
🎤 Speaker: Samuel Nartey — DevSecOps Trainer & AWS Community Builder
🎙️ Moderator: Margaret Amanfu — DevOps Engineer
Register to join us, and share this event with someone who would find it useful.