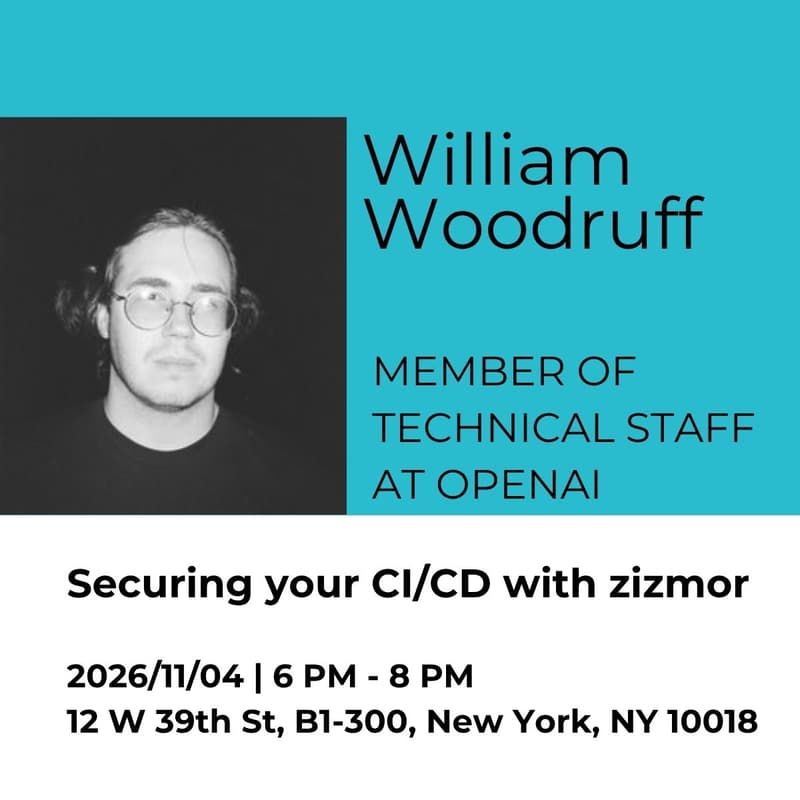
Securing your CI/CD with zizmor
We're excited to host the NYC Open Source Security User Group Meetup on Nov 11/4, 2026!
Agenda:
6 - 6:30 PM: Food and networking
6:30 - 7:30 PM: Talk -
7:30 - 8:00 PM: Mingling and wrap-up
Location: 12 W 39th St, New York, NY 10018, JFK27 B1.300
Talk: Securing your CI/CD with zizmor
Talk Description: CI/CD inhabits a critical position in both corporate and open source projects: it’s trusted to manage secrets, release processes, and many other high-integrity operations. Despite this, the security of our CI/CD setups is often an afterthought, and attackers have leveraged this in recent years to conduct large-scale supply chain attacks across GitHub and various open source packaging ecosystems. This talk walks through many of the common weaknesses found in CI/CD setups and demonstrates how we can use zizmor to find and automatically remediate many security risks.
Speaker/ Speakers: William Woodruff
Speaker bio:
William Woodruff is a Member of Technical Staff at OpenAI, where he works on high-performance, secure tooling for the Python ecosystem. Previously he worked on similar tooling at Astral; prior to that he was an Engineering Director at Trail of Bits, where he was responsible for high-impact security contributions to open source ecosystems via the open source ecosystem security group.
Outside of work, William is the primary maintainer of zizmor, a maintainer of Homebrew, Sigstore, and pip-audit, and a long-term contributor to Python cryptography (PyCA) and packaging (PyPI, PyPA). He maintains a website at yossarian.net and a blog at blog.yossarian.net.