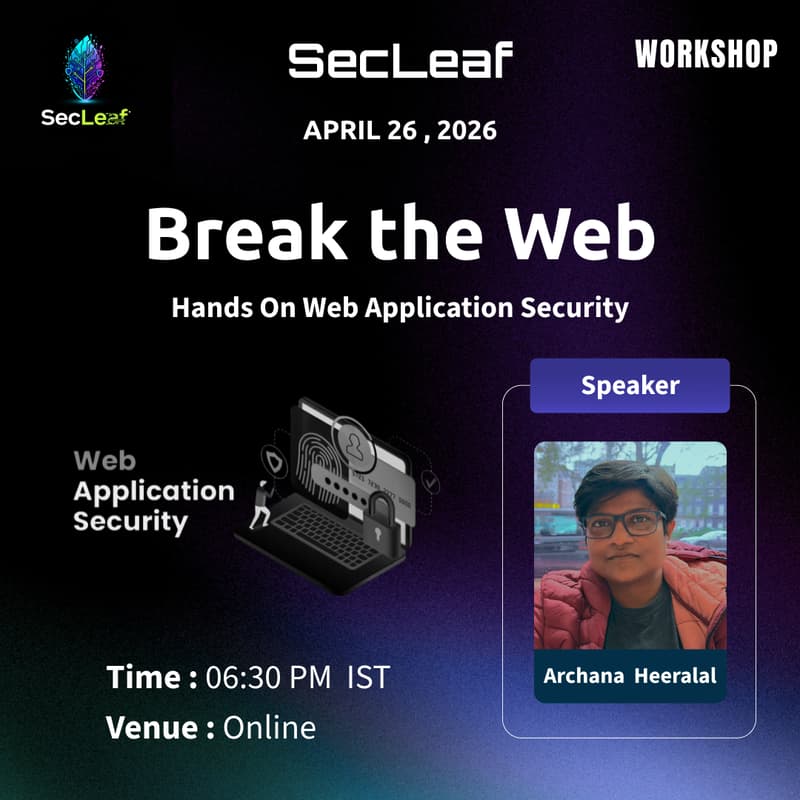
Break the Web: Hands-on Web Application Security
In this session, we’ll explore Web Application Security in action—from understanding how web applications work to identifying and exploiting real-world vulnerabilities.
What You’ll Learn
• Fundamentals of web applications and security
• How HTTP/HTTPS works (and common misconceptions)
• Overview of the OWASP Top 10 vulnerabilities
• Live demos of attacks like SQL Injection and Cross-Site Scripting (XSS)
• Hands-on experience with security testing tools
• Participate in a mini CTF challenge
• Explore career paths in application security
Join Our Community
Stay updated with session details, announcements, and cybersecurity discussions:
Join WhatsApp Group
Follow SecLeaf
Stay connected for updates, resources, and upcoming events:
https://linktr.ee/SecLeaf