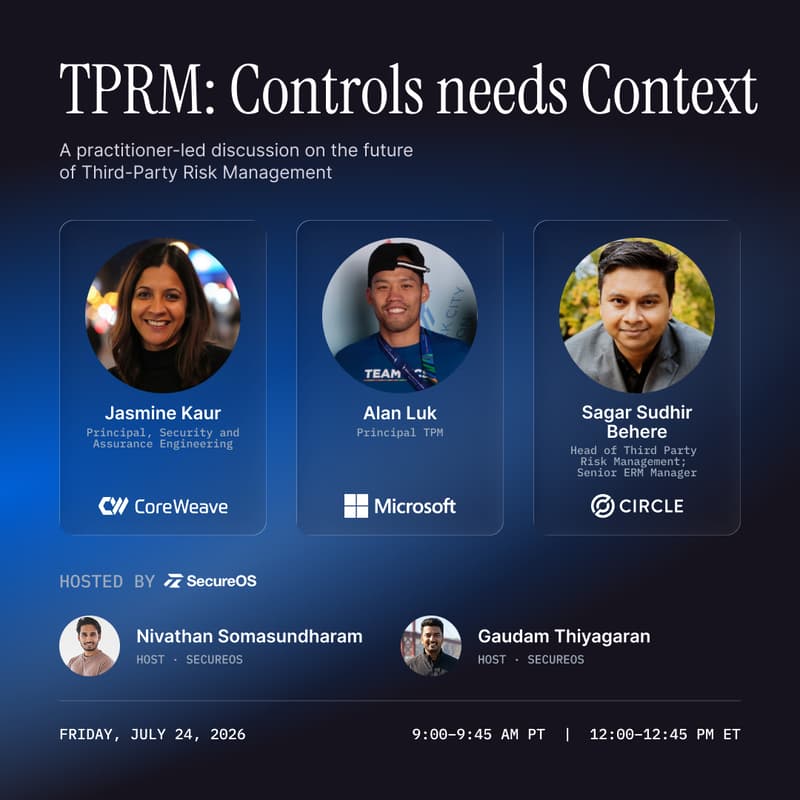

TPRM: Controls needs Context
A panel discussion on the future of Third-Party Risk Management
Third-party risk is at a turning point.
Traditional TPRM programs were built around questionnaires, periodic reviews, and manual coordination. Today's enterprises need continuous assurance, faster decisions, and better collaboration across security, procurement, legal, privacy, and the business.
Join an interactive discussion with practitioners and industry leaders as we explore how TPRM is evolving—from static controls to context-driven, autonomous execution.
This is not a product demo or a sales presentation. It's an open conversation about what's changing, what isn't, and where the industry is headed.
Discussion Topics
Why traditional TPRM operating models are breaking down
Controls vs. context: what actually drives better risk decisions
Continuous assurance beyond annual assessments
Where AI and autonomous execution deliver real value today
Human judgment, governance, and defensible decision-making
Lessons learned from building and operating enterprise TPRM programs
The future of GRC Engineering and Third-Party Risk
Panelists
Jasmine Kaur
Principal, Security & Assurance Engineering, CoreWeave | Former Google
Building next-generation Assurance Engineering and continuous security programs at hyperscale.
Sagar Sudhir Behere
Head of Third-Party Risk Management, Circle | Former Meta & EY
Leading enterprise TPRM programs and driving the evolution toward intelligence-driven, continuous risk management.
Alan Luk
GRC Engineering, Microsoft Azure | Former Head of GRC at Superhuman
A leading voice on GRC Engineering, continuous controls, and modern governance at enterprise scale.
Nivathan Somasundharam
Founder & CEO, SecureOS
Gaudam Thiyagaran
Co-Founder & CTO, SecureOS
Who Should Attend
Third-Party Risk leaders
GRC and Risk professionals
CISOs and Security leaders
Procurement leaders
Privacy and Compliance teams
Internal Audit professionals
Anyone interested in the future of enterprise risk and governance
Bring your questions. This will be an interactive discussion with plenty of time for audience participation.