
Sunburst and the SEC: Five Years on the Front Line of a Nation-State Attack.
ISC2 LA Lunch & Learn
On Saturday, December 12, 2020, Tim Brown, then CISO of SolarWinds, got the call every security leader dreads: a nation-state actor had compromised the company's build system and shipped tainted code to up to 18,000 customers. SUNBURST became one of the most closely watched cyber incidents in history. Three years later, the SEC charged SolarWinds and Tim personally, the first time a CISO had ever been charged. The case was largely dismissed in 2024 and dropped entirely in December 2025.
In this candid session, Tim covers the first hours of the response, choosing transparency over the safe legal answer, rebuilding trust with customers, and what it was like to be named personally by a regulator. He'll be honest about what they did well, where they were lucky, and what every security leader, executive and board should do now so they are ready, not lucky.
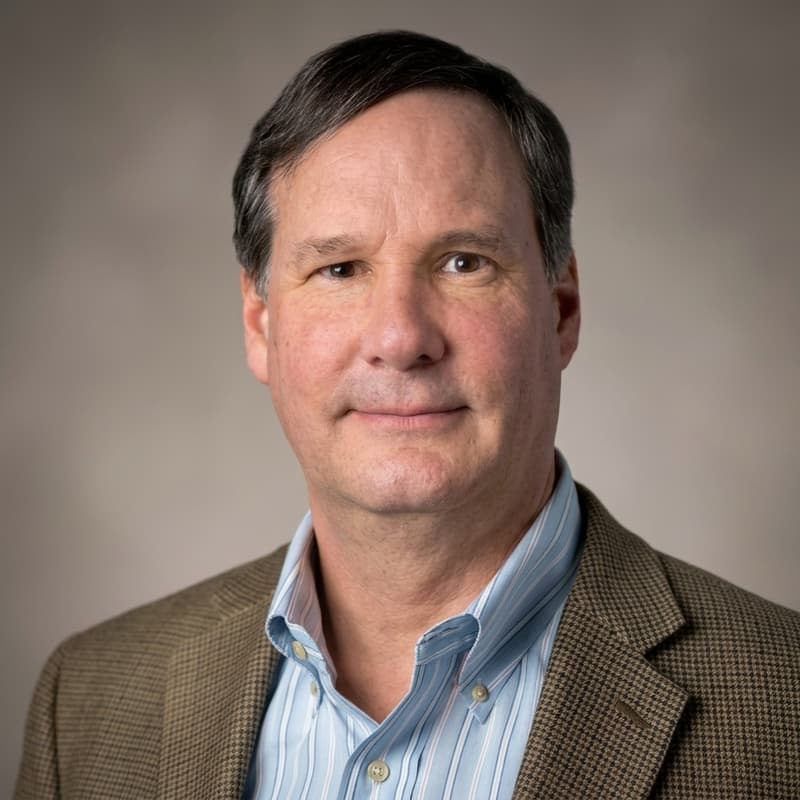
🎙️ Featured Speaker: Tim Brown
Tim Brown is Chief Strategy Officer at Cytactic and a Partner and CISO in Residence at Team8, where he leads the CISO Village. As CISO of SolarWinds, he led the response to the 2020 SUNBURST attack and the SEC action that followed. Today he is focused on taking the luck out of incident response and backing the startups that will secure our future. He holds 18 issued security patents.
📅 When: Nov 19th, 2026, 12:00-1:00 PM PST
💻 Where: Virtual—join from anywhere!
Whether you're a seasoned expert or new to the field of AI and Cybersecurity, this is your chance to learn, connect, and grow within the cybersecurity community.
#ISC2LA #CyberSecurity #InfoSec #DevSecOps #CloudSecurity #ThreatIntelligence #RiskManagement #CyberResilience #Networking #CareerGrowth